One Domain, Twelve Brands Targeted
Anatomy of a live subdomain-abuse campaign and what security teams should do about it In early April 2026 a single parent domain – offcialonlinee.
Anatomy of a live subdomain-abuse campaign and what security teams should do about it
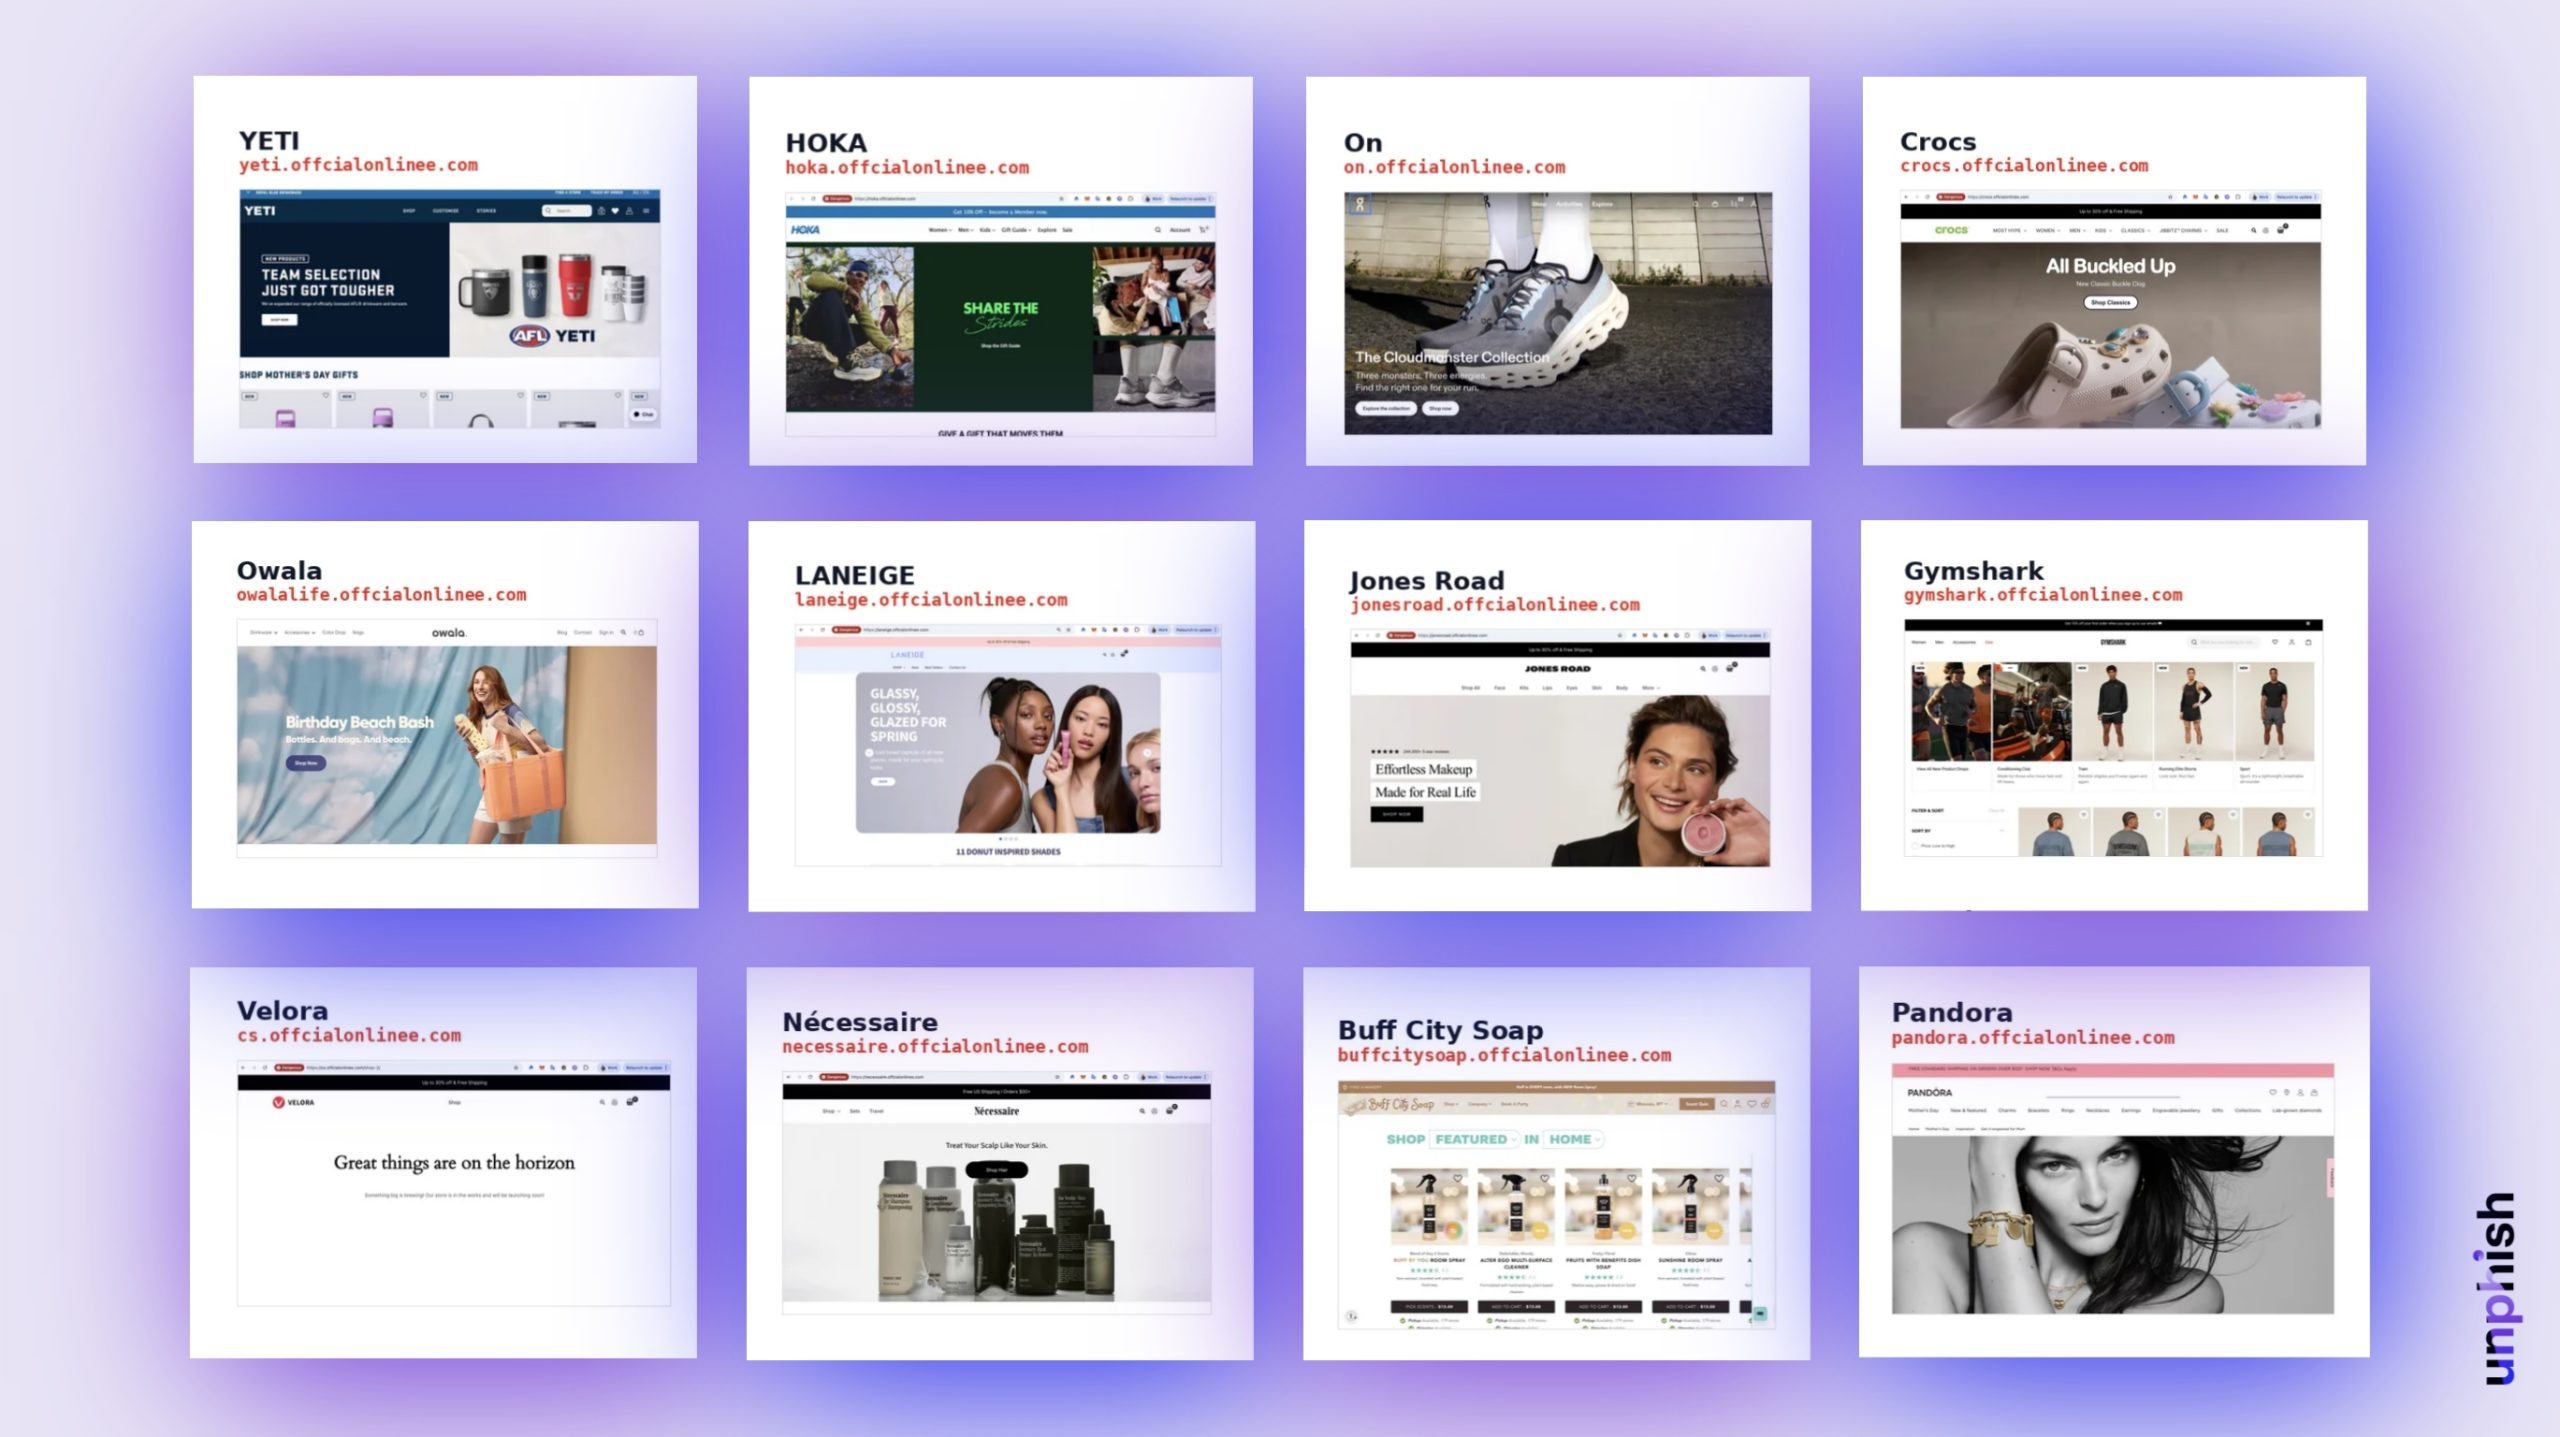
In early April 2026 a single parent domain – offcialonlinee.com – quietly began impersonating more than a dozen well-known consumer brands. Each brand was given its own third-level label: yeti.offcialonlinee.com, pandora.offcialonlinee.com, hoka.offcialonlinee.com, crocs.offcialonlinee.com, and more. Same infrastructure, same discount banner, same store template – different logo. It is one of the cleanest live examples of subdomain abuse we have seen this quarter, and a useful reminder that brand impersonation is now an economies-of-scale business.
What is subdomain abuse?
Subdomain abuse is a phishing and fake-storefront technique where a single registered domain is used as a launchpad to attack many brands at once. Instead of registering twelve separate domains – twelve WHOIS records, twelve TLS certificates, twelve takedown targets – the attacker registers one “base” domain and spins each brand up as a subdomain underneath it.
Three things make this pattern attractive to attackers:
- Operational leverage. One DNS zone, one wildcard TLS certificate and one hosting stack serves every brand page.
- Cheap rotation. A burned subdomain is replaced in seconds; no registration, no ICANN paperwork, no new certificate.
- Takedown friction. Each victim brand usually only sees its own subdomain, so the defender workload is fragmented across many uncoordinated reporters.
Case study: offcialonlinee.com
The parent domain is a classic typosquat of “official online” with two deliberate misspellings designed to survive a casual glance at a URL bar or an email preview. Our passive-DNS monitoring has surfaced the following subdomains over roughly six weeks – each one staged as a fully-themed fake storefront:
| Subdomain | Impersonated brand | First seen | Last update |
|---|---|---|---|
| www.offcialonlinee.com | Staging / template shell | Mar 16, 2026 | Mar 23, 2026 |
| cs.offcialonlinee.com | Placeholder (“Velora” / shop-2) | Apr 3, 2026 | Apr 4, 2026 |
| hoka.offcialonlinee.com | HOKA (footwear) | Apr 5, 2026 | Apr 5, 2026 |
| laneige.offcialonlinee.com | Laneige (beauty) | Apr 7, 2026 | Apr 7, 2026 |
| jonesroad.offcialonlinee.com | Jones Road (cosmetics) | Apr 7, 2026 | Apr 7, 2026 |
| buffcitysoap.offcialonlinee.com | Buff City Soap | Apr 7, 2026 | Apr 7, 2026 |
| necessaire.offcialonlinee.com | Nécessaire (body care) | Apr 7, 2026 | Apr 7, 2026 |
| owalalife.offcialonlinee.com | Owala (drinkware) | Apr 13, 2026 | Apr 13, 2026 |
| yeti.offcialonlinee.com | YETI (drinkware) | Apr 14, 2026 | Apr 14, 2026 |
| on.offcialonlinee.com | On (running footwear) | Apr 15, 2026 | Apr 16, 2026 |
| pandora.offcialonlinee.com | Pandora (jewelry) | Apr 15, 2026 | Apr 15, 2026 |
| gymshark.offcialonlinee.com | Gymshark (apparel) | Apr 15, 2026 | Apr 18, 2026 |
| crocs.offcialonlinee.com | Crocs (footwear) | Apr 17, 2026 | Apr 18, 2026 |
Every subdomain uses the same visual template: an “Up to 30% off & Free Shipping” sale banner, a centered brand logo pulled from the genuine brand, a headline marketing image, and a checkout flow that collects card details. Chrome Safe Browsing flags most of them as “Dangerous” in the address bar, so Google has already correlated several.
Two observations worth calling out:
- on.offcialonlinee.com impersonates On Running, while cs.offcialonlinee.com on the same host briefly returned a different brand shell (“Velora”) and a /shop-2/ path - a sign the operator is A/B-testing or rotating brands on the same infrastructure.
- The oldest subdomain - www.offcialonlinee.com, first seen March 16 - looks like the operator’s staging shell. Every brand subdomain that followed reuses the same template and URL structure (e.g. /product-category/shop/).
Underneath the visual theming the plumbing is boring and reusable. A single wildcard TLS certificate issued against .offcialonlinee.com is enough to serve every brand page with a valid padlock. The same IP, the same Apache or Nginx configuration, the same payment-capture form and the same WooCommerce-style /product-category/ path structure appear across every subdomain we inspected. That reuse is the whole point: the operator has reduced the marginal cost of attacking a new brand to roughly the time it takes to swap a logo and a hero image.
Why it works
From a consumer perspective the attack is simple and highly convincing. The brand name in the subdomain label (“yeti”, “pandora”, “hoka”) matches the brand in the logo, and most users do not parse hostnames right-to-left. A quick glance at “yeti.offcialonlinee.com” reads as “YETI.” Mobile browsers, email clients and chat apps make this worse by truncating or hiding the full hostname entirely.
From a defender perspective the architecture exploits a gap in how we are organized. Brand teams monitor mentions of their brand and typically only see yeti. Security teams monitor their own domains, not other brands’. Unless someone is watching the parent domain – or watching Certificate Transparency for wildcard issuances under it – the victim brands end up fighting twelve separate, overlapping battles.
Detection and response for security teams
Signals worth monitoring:
- Certificate Transparency. Alert on any certificate whose SAN contains your brand as a left-most label under a domain you do not own. Wildcard certs for the parent often precede the brand subdomain going live by hours.
- Passive DNS. Watch for NXDOMAIN - A flips on $brand under suspicious parents, especially freshly-registered typosquats of generic e-commerce terms (official, online, shop, outlet, store).
- Typosquat keyword monitoring. offcialonlinee.com drops one letter from “official” and adds an extra “e” to “online” — two of the most common registrar-permitted variations, and the pattern repeats across campaigns.
For takedown and response:
- Target the parent, not just the subdomain. Report offcialonlinee.com to its registrar’s abuse contact, its hosting provider, Google Safe Browsing, Microsoft SmartScreen, APWG and the CERT in the hosting jurisdiction.
- Coordinate with the other victims. Twelve fragmented complaints become one consolidated escalation that registrars and hosts respond to far more aggressively. A shared spreadsheet and a single point of contact is often enough.
- Block at the edge. Push offcialonlinee.com into corporate DNS RPZ feeds, email-gateway blocklists and secure-browsing policies for staff so that whoever wanders into the next subdomain is caught before they convert.
The takeaway
Subdomain abuse is not new, but offcialonlinee.com is a useful snapshot of how mature the tradecraft has become. One registration, one template, one operator, twelve brands – and almost certainly more before the infrastructure is taken down. Defending against it means moving the monitoring target one level up: from your own domain to any domain capable of becoming the parent for yours.
This article was prepared by the Unphish team based on live monitoring data collected between March 16 and April 24, 2026.